Role-based access
Access is role-based. Each role is given what it may see and do.
Who can do what in Xpense is decided by role, and what they did is logged. This page lists the controls and how to reach us about security or privacy.
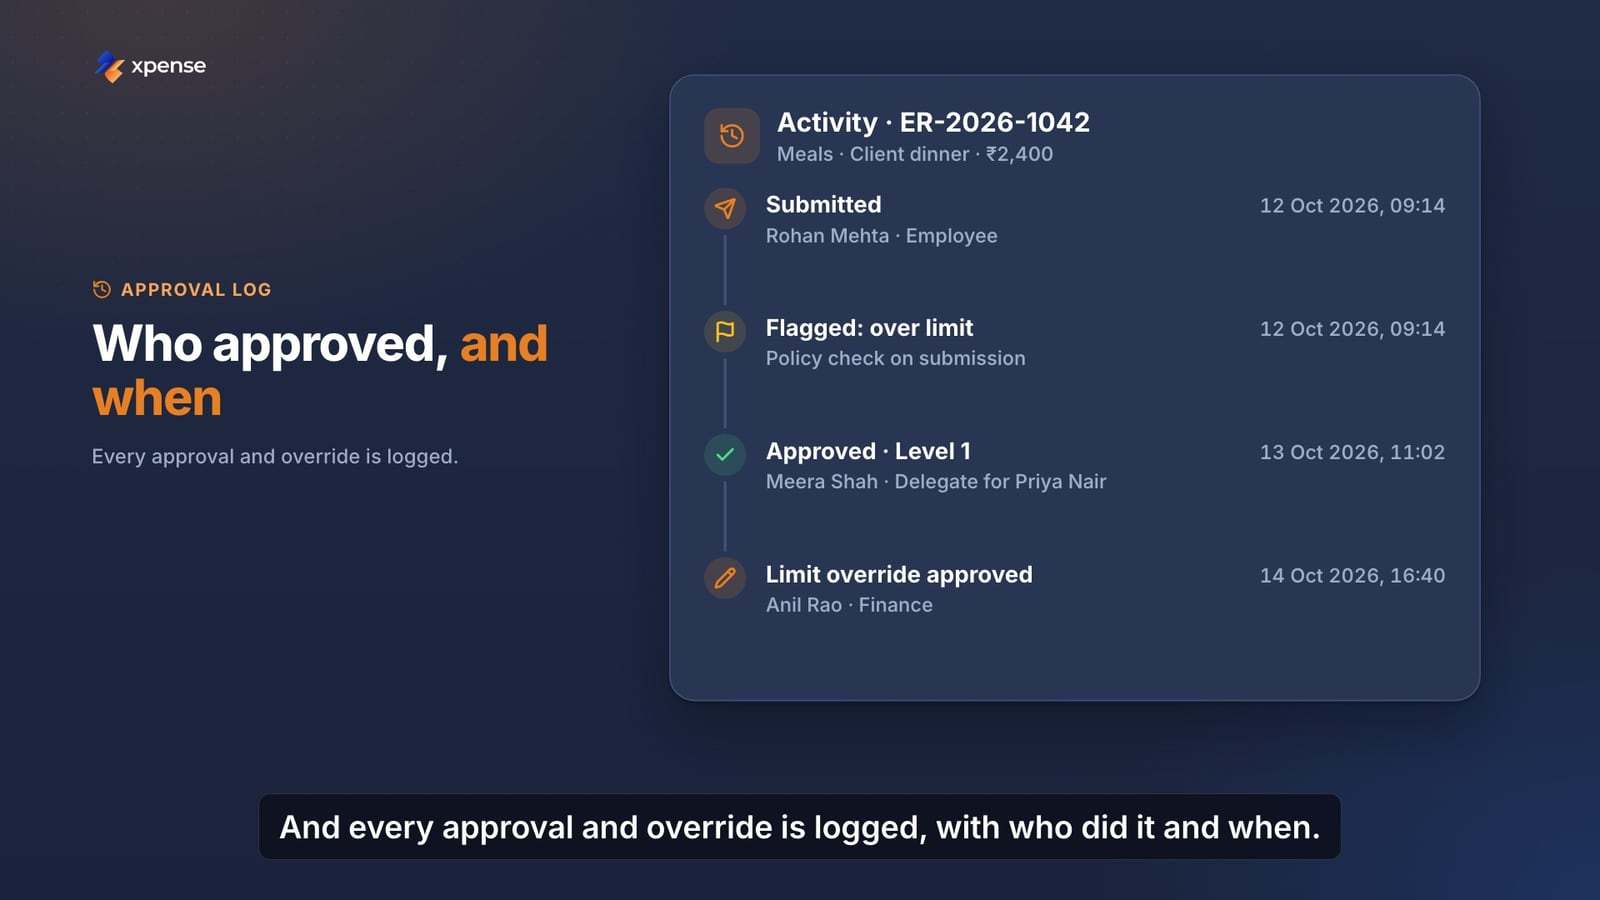
Access is role-based. Each role is given what it may see and do.
Approvals and actions are logged.
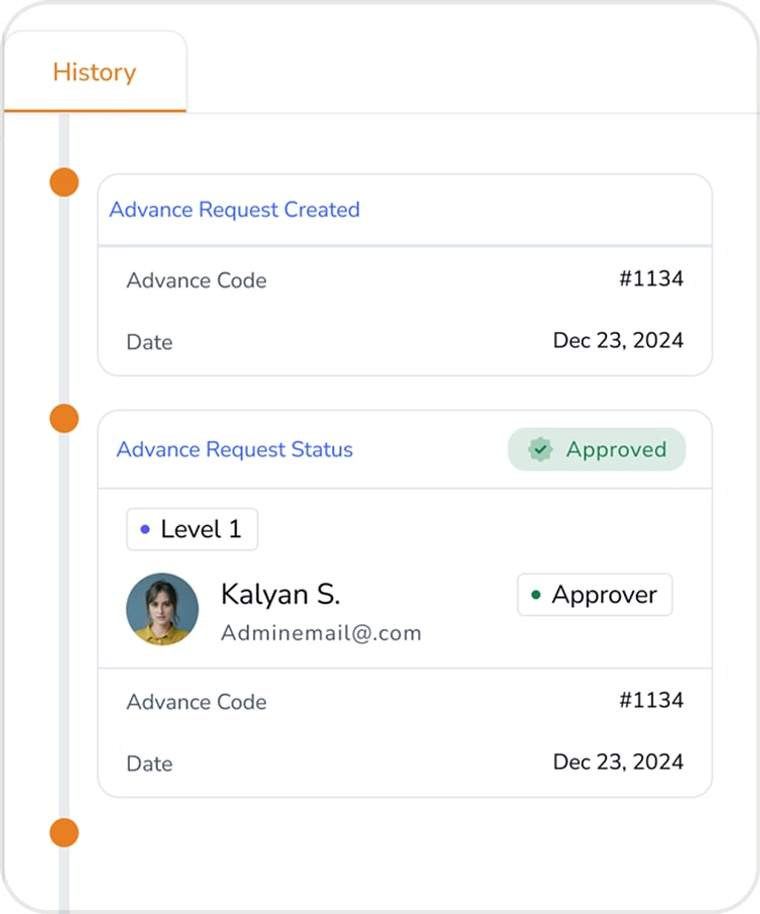
Every trip, expense and advance has a timeline.
Sign in with Microsoft is available.
Integration credentials are encrypted at rest.
AI features are switched on per company from an AI control plane, and AI usage is metered with plans and budgets.
Employees sit in your company structure: group, company, business unit, plant, cost centre. Their role decides which trips, claims and reports they can open and what they can do with them.
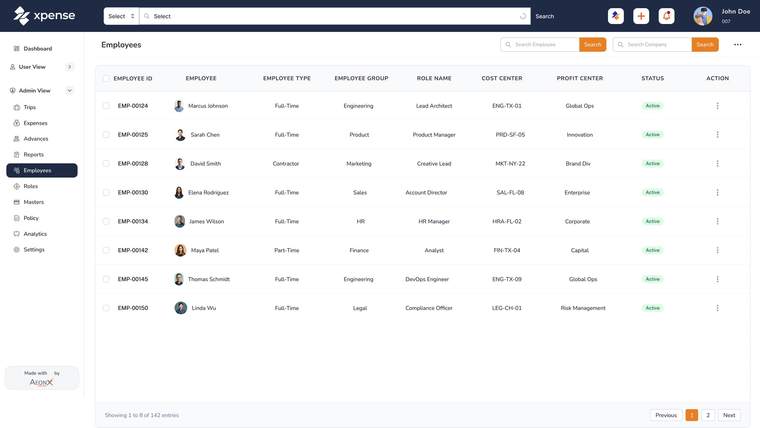
Approvals and actions are logged. A trip, an expense or an advance can be opened to see its timeline: each step, who took it and when.
Xpense has an MCP server for AI assistants and agents. Every MCP call carries the employee's own sign-in token and is bound to one company, so an assistant can do only what that employee can do.
Xpense is built and run by AeonX Digital.
AeonX Digital is certified to ISO/IEC 27001, ISO 9001 and ISO/IEC 20000-1.
Access is role-based. Finance decides what each role can see and do.
Sign in with Microsoft is available.
Integration credentials are encrypted at rest.
AeonX Digital is certified to ISO/IEC 27001, ISO 9001 and ISO/IEC 20000-1.
Only what the signed-in employee can. Every MCP call carries the employee's own sign-in token and is bound to one company.
Write to privacy@aeonx.digital.